Dark-web OSINT · hosted · open source
Dark-web threat intel
in your browser.
Ask one question. VoidAccess searches 12+ Tor search engines, GitHub and security feeds in parallel, then gives you back actors, wallets, leaked credentials and IOCs, ready to export as STIX, MISP or Sigma. No Tor to run. Nothing to install.
100 free credits a month · no card · from $7/mo after that
Open source (MIT)896★ on GitHub18k+ downloadsBuilt by Katriel Moses, who found CVE-2026-50112 (Apache CloudStack RCE)
What people use it for
Is your company on a leak site?
Search your domain and brand across dark-web search engines and GitHub. See what's being said before an attacker acts on it.
Track a ransomware group
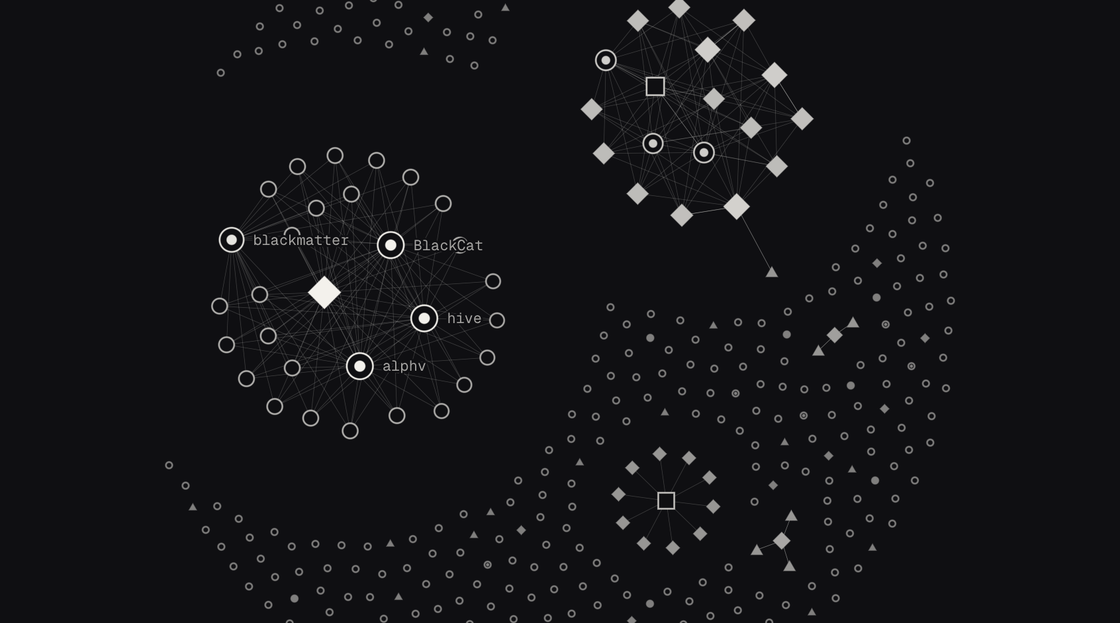
Map a group's .onion sites, wallets, handles and the CVEs it exploits, and see how they connect.
Turn a lead into detections
Start from a handle, a wallet or a hash. End with IOCs and Sigma, YARA or Suricata rules your SIEM can load.
See what was there before
Findings from earlier investigations stay in the VoidAccess archive, dated, so you can still see infrastructure that has since gone offline.
For security researchers, threat-intel teams, MSSPs and authorised investigators.
12+ Tor search engines and public threat intel, searched at once.
One query fans out from our servers through Tor and follows new .onion links as it finds them. You never touch Tor yourself.
Tor search engines
Torch, Ahmia, Tor66 and 9+ more.
Threat intel
Indicators checked against public threat-intel sources.
GitHub
Leaked keys, tooling, configs.
Security feeds
Headlines and snippets from research feeds.
Curated .onion seeds
Known starting points, followed recursively.
Checked against public sources including CISA KEV, NVD, MITRE ATT&CK, crt.sh, RDAP and the Wayback Machine.
From question to report in one run.
- 01
Ask
Type a question in plain English. The AI sharpens it before anything is collected.
- 02
Collect
Dark-web search engines, GitHub and security feeds are searched in parallel through Tor.
- 03
Filter
Noise, duplicates and prohibited content are dropped automatically.
- 04
Extract
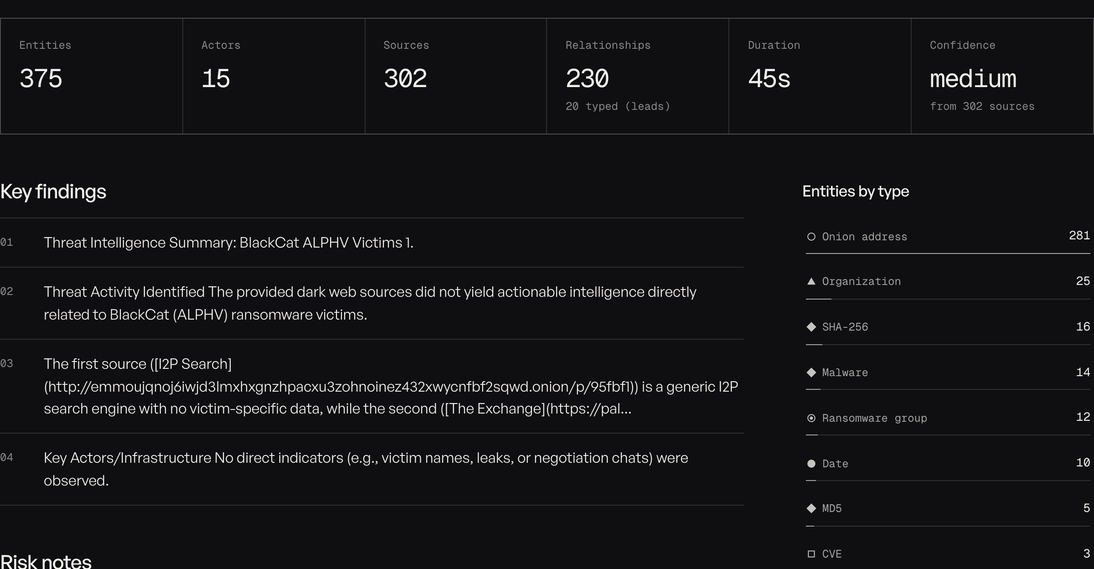
Actors, wallets, credentials, CVEs and IOCs are pulled out and cross-checked.
- 05
Deliver
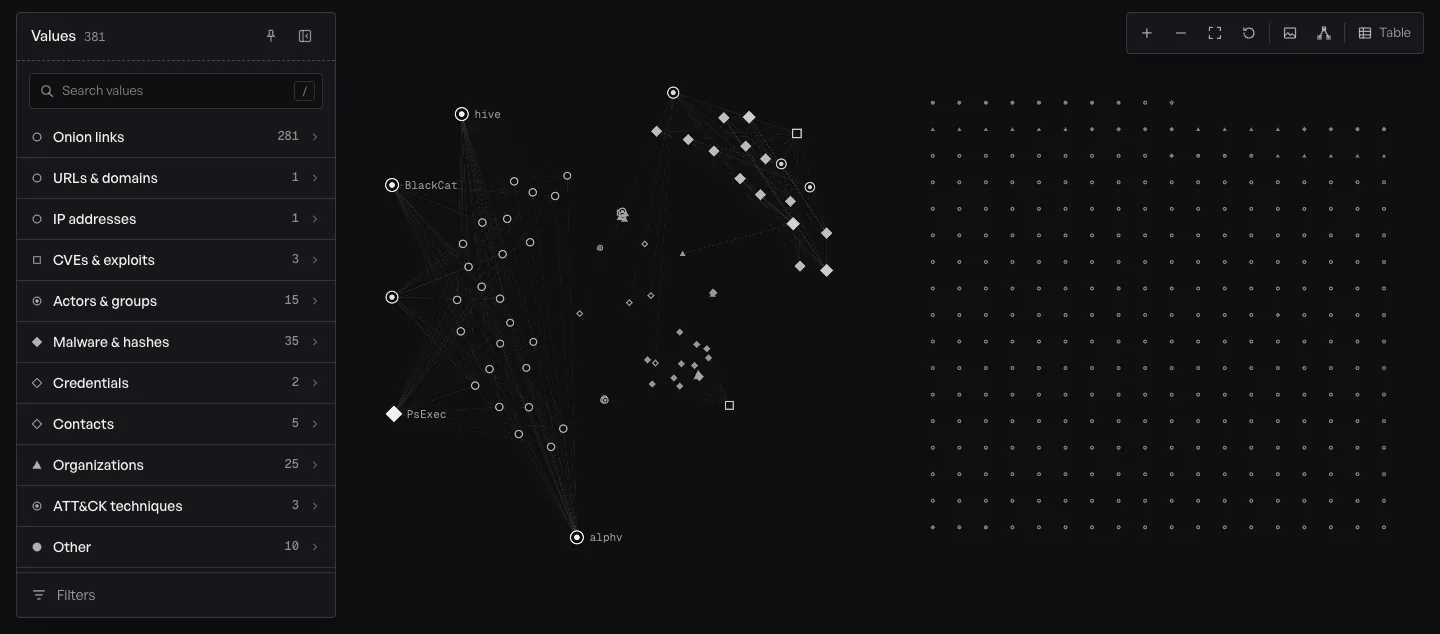
You get a summary, a searchable relationship graph and an export-ready result.
It pulls out what analysts actually need.
Pattern matching, entity recognition and optional AI analysis, cross-referenced against earlier findings. Values below are defanged samples.
LockBitSuppLockBit 3.0CVE-2023-4966bc1q…k7x2@ransom_opssvc_backup:••••••lockbit…[.]onionThis is what you get back.
Nine formats for the tools you already run.
STIX 2.1 and MISP for sharing. Sigma, YARA, Snort and Suricata for detection. CSV, JSON and Markdown for everything else. CSV and JSON are on every plan, including Free.
Enterprise threat-intel output without the enterprise price.
| Enterprise dark-web intel platforms | VoidAccess | |
|---|---|---|
| Price | From ~$40k a year, sales call first | Free, then from $7/mo |
| Setup | Procurement and onboarding | Sign in and search |
| STIX / MISP export | Yes | Yes |
| Open source | No | Yes, MIT. Self-host free forever |
They have closed-forum access, analyst teams and years of archives. We don't. VoidAccess is for researchers and small teams who need answers today, not a contract.
Open source at the core.
The engine is MIT-licensed on GitHub with 896★. Run it yourself for free, or skip setting up Tor, Docker and API keys from $7 a month.
Questions security teams ask first
Is this legal?
VoidAccess searches publicly reachable sources: Tor search engines, code hosts and public threat feeds. It doesn't log into closed forums or buy data. Every account agrees to our Acceptable Use Policy, which limits use to security research and authorised investigation.
Will it show me illegal content?
Safety filters block prohibited queries, links and page content before anything reaches you, and results never link to dark-web pages. Found addresses are shown as text you can copy, not links.
What happens to my queries?
Your investigations are kept while your account is open and deleted when you delete it. Queries and collected text go to our AI providers to refine the search and write the summary, never with your account details. Findings go into an anonymous, dated archive that never contains your identity or your query text. Read the privacy policy.
Who is it not for?
Stalking, doxxing, harassment, or anyone looking for illegal content or services. We close accounts that try.
Can I self-host instead?
Yes. pip install voidaccess, MIT licence, free forever.
What will you hunt today?
Hosted, nothing to install. 100 free credits every month, about 5 Quick or 2 Standard investigations. No card.